Multi-tier AWS environment with Terraform
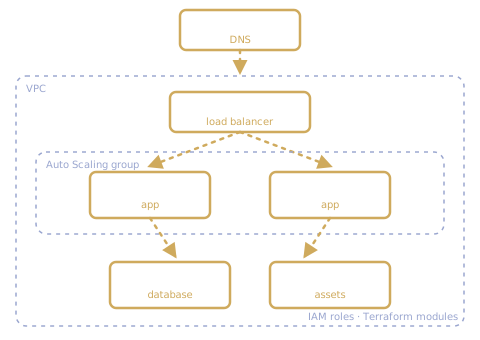
Traffic enters through Route 53 and an Application Load Balancer that spreads requests across EC2 instances in an Auto Scaling group inside a dedicated VPC. Application data is stored in Amazon RDS and static assets in S3, with access controlled by IAM roles.
The whole environment is described as Terraform code with reusable modules and variables, so it can be created, changed and destroyed reproducibly.
Results
- 8 AWS services in one environment
- Scales out automatically with load
- Fully reproducible with Terraform modules