This website — secure Flask portfolio with CI/CD
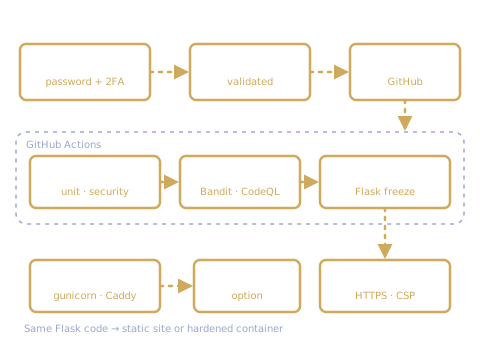
Content is edited in a private admin panel (password + two-factor login, CSRF protection, rate limiting, audit log) and stored as validated JSON.
Every push runs GitHub Actions: 44 unit and security tests, Bandit and pip-audit, CodeQL scanning and a Docker build. The same Flask code is then frozen into a static site and deployed to GitHub Pages with a strict Content-Security-Policy. For a custom domain it ships as a hardened container: non-root, read-only filesystem, gunicorn behind Caddy with automatic HTTPS.
Results
- 44 automated tests on every push
- Deployed automatically by GitHub Actions
- No cookies, no trackers, strict CSP